 Nadine Freischlad · · 3 min read
Go-Jek’s app has major data leaks, claims security firm. Go-Jek says they’re fixed.
Indian security firm Fallible claims to have exposed major security flaws in Go-Jek – Indonesia’s highest valued startup on record and a rival of Grab and Uber in the country. Go-Jek claims the issues have been fixed.
Fallible revealed its discoveries in a blogpost on Hackernoon. It specializes in detecting flaws in API end-points – the interface tech companies set up so that other services can exchange data with them. If not secured properly, APIs can lead to leaks, where private data can be extracted in unintended ways.
Fallible claims it was still able to extract ride history data and customer order data a few days ago.
In the case of Go-Jek, Fallible says, it was able to extract information from a ride history API which let it read a list of all rides taken by any user, including GPS coordinates of the ride.
The security firm also claims to have been able to exploit a vulnerability to see details of orders customers made through the app. It even found a way to potentially meddle with notifications users receive.
Another problematic API revealed user data, including phone numbers, pickup and drop off points – but this leak has now been patched, Fallible tells Tech in Asia.
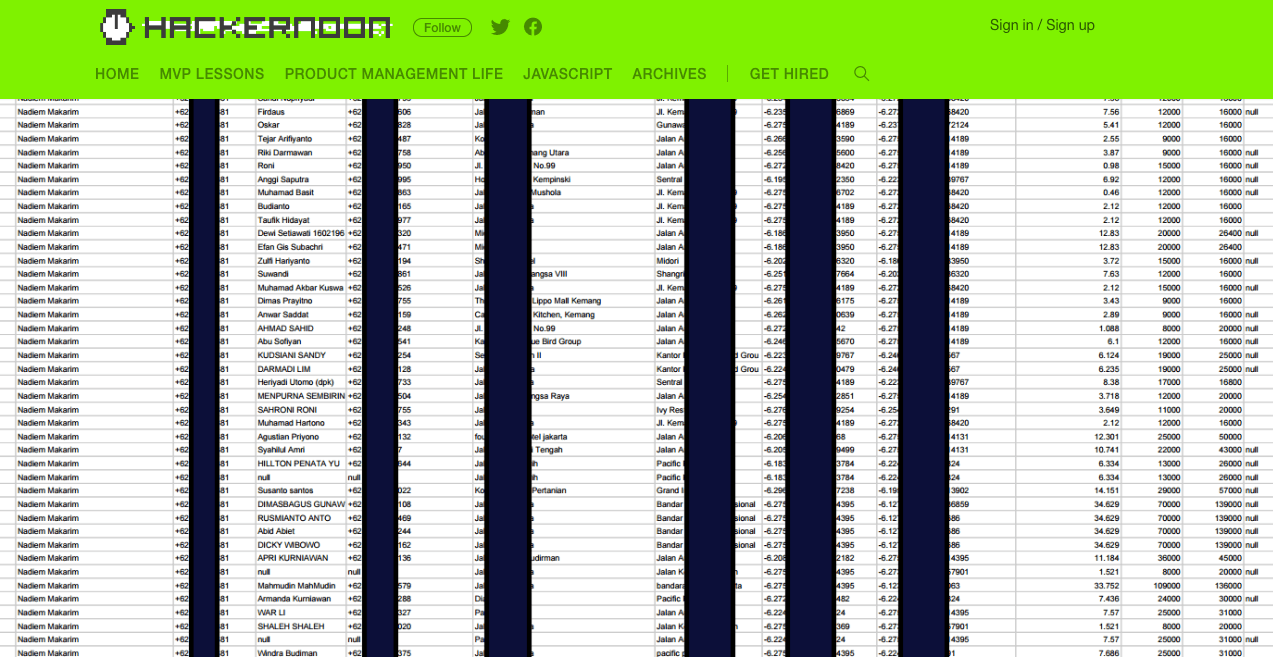
Indian security firm Fallible revealed some of the data it was able to obtain in an article on Hackernoon.
The others were still supposedly pending at the time the Indian firm decided to publish its findings a few days ago, after giving Go-Jek several months to address its security flaws.
Disagreement over what’s been fixed
Go-Jek chief information security officer Sheran Gunasekera argues a different timeline.
He says the data leaks were all addressed and fixed at the end of July, shortly after Fallible first contacted the firm in June.
“I am not claiming we are perfect, but we take the protection of our customer’s data seriously,” says Sheran.
Having worked in information security for 15 years, he agrees it’s a common industry practice to hunt for flaws in big tech companies like Go-Jek. He values the type of responsible disclosure Fallible did.





Stay updated on the go with our mobile app.
Get latest insights with smoother, more personalized experience through TIA mobile app.






📅 Upcoming Events
22 October 2026
Payoneer x CSPN Summit 2026