 Leighton Cosseboom · · 4 min read
Warning: tech startups should take cyber security seriously, and here’s why
Image from Cuneopost
Last week, Tech in Asia picked up a story about a hacker in Thailand who spotted gaping security holes in Indonesia’s on-demand motorcycle app Go-Jek. According to the programmer, the bugs could allow anyone with the right knowledge and a simple web browser to infiltrate the company’s system, and change around all sorts of things like email addresses, phone numbers, user names, and even the virtual credit of drivers and partnering vendors.
The bugs reportedly existed for several months before the hacker decided to make the information public. Local media had a field day with the discovery.
The incident generated some heat for Go-Jek but also raised larger questions about whether startups should be more careful about cyber security. Go-Jek is unquestionably one of Indonesia’s largest and most talked-about tech firms. It has seen incredible growth and taken on multiple large funding rounds. Many would argue that the company is no longer a “startup” in the strictest sense of the word. Young tech firms are undoubtedly taking cues from the nation’s “Uber for motorcycles.”
In the recent past, Indonesia has been cited as the capital of the world for cyber attacks. Back in 2013, US-based Akamai Technologies published a report saying the archipelago is now responsible for 38 percent of the world’s malicious traffic. Odds are, that number has grown.
After polling readers on the Tech in Asia Community Facebook page, I was able to dig up a couple of interesting cautionary tales of startups that didn’t stay on top of their cyber security, sometimes sacrificing user data protection for agility in their competitive markets.
See: Confirmed: Sequoia Capital invested in Indonesia’s Go-Jek
A stalker’s delight
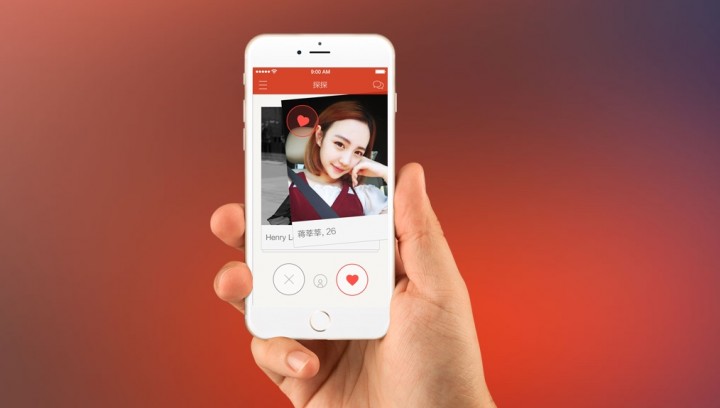
One of our users shared a news article about an app called Tantan. The startup, which is essentially a Tinder clone for China that raised a US$5 million series A funding round last year, had a basic security flaw. It sent passwords, phone numbers, location data, and more via plain text back and forth from the app in a user’s pocket to the company’s server.
The problem, according to tech blog Motherboard, was that pretty much any communication between the app and the Tantan server in China was sent unencrypted. This meant that anyone sitting at a cafe with a wifi connection and a little bit of IT knowledge could pluck user data from the air if they felt like it.
In addition to knowing someone’s hometown, sexual preference, and other tidbits of personal information, hackers could triangulate (in a manner of speaking) the actual location of any user with the app. Tantan sent this data to the server sometimes several times per minute. The data could then easily be plugged into Google Maps to track someone’s whereabouts.
You may be wondering, “Why would anyone go through the trouble? Don’t people have better things to do?” The answer is: yes most people do. But not everyone. Consider the nature of an app like Tantan. This security flaw could allow users to stalk other users, regardless of whether they’ve already been blocked. Someone scorned by romantic rejection could decide to access sensitive data about the other person, then use it any way they please.
Bitcoin bank robbery





Stay updated on the go with our mobile app.
Get latest insights with smoother, more personalized experience through TIA mobile app.






📅 Upcoming Events
22 October 2026
Payoneer x CSPN Summit 2026