This article is a part of Startup Spotlight, a series that features young, up-and-coming startups.
Image credit: Timmy Loen
The founders of AppSecAI used AI to write a country-western song, then tested it on something riskier, finding and exploiting software vulnerabilities. The results were surprising enough to convince them that the same capability needed to be turned toward defense instead of attack.
Realizing the threat automated AI attacks now pose to enterprise software, they built a platform that uses AI to automatically fix security flaws instead of just finding them.
😟 Problem
Enterprises currently spend an average of US$10,000 and 272 days to manually remediate a single software vulnerability. Companies carry tens of thousands of these expensive flaws across legacy systems.
The release of advanced AI models has turned this backlog into an enterprise emergency. These tools allow threat actors to exploit vulnerabilities at scale. Security teams lack the resources to counter these automated attacks manually.
💡 Solution
The platform integrates into existing deployment pipelines on GitHub to deliver code fixes to engineering teams. The technology offers several distinct capabilities, including:
- Automatically generates necessary code patches when a vulnerability is detected.
- Creates a workflow where developers verify functions while security validates fixes.
- Reduces an 11-step manual process into an automated workflow completed in minutes.
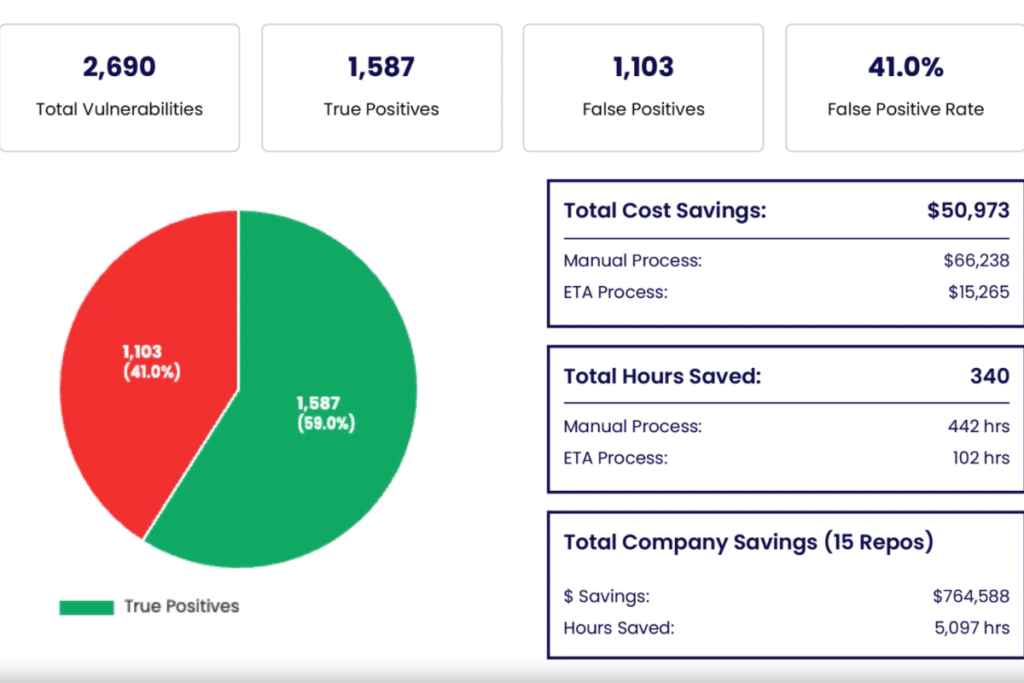
Image credit: AppSecAI
📊 Market size
The global application security market is projected to reach US$14.1 billion in 2025. Industry forecasts expect this figure to double by 2030. The company targets a US$250 million segment based on a conservative five percent penetration rate.
🤝 Team
- Bruce Fram. CEO. He has served as a six-time venture-backed chief executive and founding CEO of US$1.5 billion unicorn Contrast Security.
- Kevin Fealey. CTO. Former chief information security officer with leadership experience at Ernst and Young and Bullish.
- Michael Cartsonis. CPO. He has cybersecurity leadership experience, holds multiple patents, and has served as chief product officer at Contrast Security.
🚀 Traction
- Reduces remediation time from 272 days to 30 minutes, cutting costs from US$11,000 to US$250.
- Achieved highly favorable unit economics with US$0.10 cost of goods sold per fixed vulnerability.
- Onboarding more than 100 target customers through OWASP-OASIS.org open-source proof-of-concept initiatives.
- Secured commercial deals while maintaining zero customer acquisition costs via industry partnerships.
🏆 Competition
Legacy security tools like BlackDuck focus exclusively on finding vulnerabilities. Developer tools such as Snyk still require manual intervention from engineers.
💰 Financials
🚩 Risks





Stay updated on the go with our mobile app.
Get latest insights with smoother, more personalized experience through TIA mobile app.